 E-Paper
 Sign In




Who will trust crypto? Petr Sergeev on building infrastructure that regulators and banks can rely on
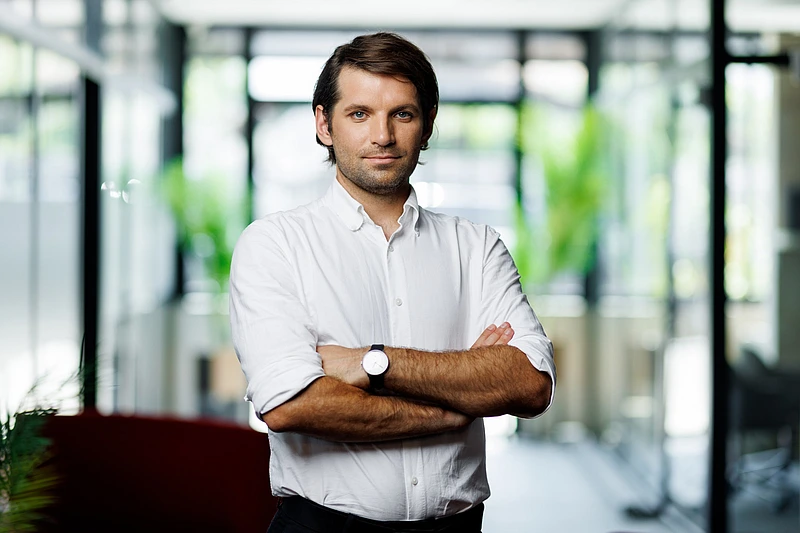
As Guardarian looks to expand in the UAE, CEO Petr Sergeev discusses licensing, banking relationships and why regulatory compliance is becoming central to crypto infrastructure
- Partner Content
- Share:


In a sector often dominated by speculative noise and rapid market cycles, creating financial infrastructure that can survive and thrive requires a unique mindset. Petr Sergeev, a serial entrepreneur and the CEO of Guardarian, a non-custodial payment solution for Web2 and Web3 businesses, discusses what it takes to build for the long term.
Given his Norwegian roots and Estonian operational foundation, Sergeev bridges the gap between traditional finance (Web2) and decentralised technology (Web3). As a technical founder, he approaches company building not as a sprint to capture momentum but as a calculated engineering discipline focused on regulatory integration, institutional reliability and systemic efficiency.
As the regulatory landscape evolves across Europe and the Middle East, his company is working towards new banking relationships and regional licensing. In this interview, he discusses the realities of building in a regulated industry, the differences between European and UAE frameworks and why infrastructure companies need to think beyond the next market cycle.
Crypto companies have spent years competing on speed, product features and access to new markets. How has that equation changed now that licensing and compliance are becoming central to the business?
The change is quite significant. A company can have an excellent product, but if it cannot secure banking services, meet regulatory requirements or build solid relationships with partners, it may struggle to operate effectively.
For us, regulation is part of the business model. The effects of our strategic plan influence our operations, the services we can provide, the structuring of our partnerships and the internal developments we need.
Technology is only one part of the equation; a legal and operational foundation is also necessary to support it. This distinction sets financial infrastructure apart from many other technology businesses.

A lot of founders view licensing as merely a cost of doing business. At what point does it become a strategic decision about where and how a company can grow?
It becomes strategic quite early, and that strategic element should not be overlooked. It influences access to banking, the types of customers you can serve and the partners you can work with. It even has an impact on how you plan to expand.
The wrong setup can create limitations that are difficult to rectify later. You may need to restructure your business, change your operating model or establish new relationships from scratch.
We view licensing as part of the company’s architecture. It should support the business you want to build rather than simply permit you to operate in one market.
What does a regulatory framework need to get right for a fintech or crypto company to build around it?
At the end of the day, trust is what enables fintech and cryptocurrency infrastructure to grow, even though transparency is also crucial. A strong framework fosters institutional trust and outlines expectations. Before opening bank accounts or integrating payment systems, financial institutions and traditional partners rely on official regulatory documents, approvals and ongoing oversight to assess compliance.
The best frameworks support innovation while maintaining precise guidelines for operational responsibility, risk management and customer protection.
Guardarian has its roots in Estonia. How has operating in the European Union shaped your approach to licensing and compliance?
To develop sustainable financial infrastructure, it is essential to keep up with significant legislative changes, such as the Markets in Crypto-Assets (MiCA) framework. Estonia provided us with a strong digital-first foundation, but navigating the EU’s evolving ecosystem taught us that local licences are only the baseline.
Preparing for and obtaining a MiCA CASP (Crypto-Asset Service Provider) authorisation requires more than just filing paperwork; operational controls, capital reserve needs, governance and AML policies must all align with the ESMA criteria. Our compliance-first approach was shaped by operating under stringent EU inspections, ensuring that our governance and risk models are prepared to provide seamless passport services across member states as MiCA establishes a common standard throughout Europe.
You are expanding into the Middle East, focusing on the UAE. What made this market worth investing in, rather than simply serving it from Europe?
Although the UAE has built a world-class financial ecosystem, entering the market properly requires a deep commitment to active regulatory compliance through local bodies like the Virtual Assets Regulatory Authority (VARA) in Dubai.
Securing the appropriate VARA Full Market Product (FMP) or VASP licences is key to serving the region effectively, rather than relying on remote integration. This process involves meeting strict requirements regarding local governance, operational presence, client asset segregation and rigorous risk management frameworks. Obtaining local authorisation enables us to establish direct institutional relationships, integrate local fiat rails and provide long-term infrastructure that aligns with the region’s regulatory requirements.
For us, the decision revolves around fostering relationships and developing infrastructure in a market where we perceive long-term potential. It’s not just about opening another office.
What do regulatory frameworks in the EU and the UAE have in common, and what ultimate objective do they both serve for the crypto industry?
While the EU (under MiCA) and the UAE (under VARA and Central Bank regulations) approach implementation differently, their core objective is identical: to bring trust, transparency and consumer protection to digital assets through structured oversight.
Both frameworks aim to eliminate regulatory arbitrage by replacing fragmented rules with comprehensive, standardised compliance requirements. Whether in Europe or the Middle East, the target is the same: establishing institutional-grade standards for risk management, capital stability, operational integrity and AML/CFT compliance. For infrastructure providers, success in both regions depends on building robust, compliance-first architecture that bridges traditional finance and Web3 with full legal clarity.
What are Guardarian’s immediate priorities in the UAE? Are you looking at a specific licence, banking partnerships or both?
Our priorities include establishing local banking rails and securing the necessary regional licences.
Building relationships and infrastructure to support fiat-to-crypto and crypto-to-fiat transactions in the UAE is essential. This involves collaborating with local financial institutions and determining how our non-custodial model aligns with the market.
Our goal is to create a reliable connection between traditional financial services and digital assets with the proper regulatory and operational foundation.
You have described Guardarian as a non-custodial infrastructure provider. What does that model mean for your regulatory responsibilities, and where does the responsibility lie between Guardarian, its partners and the customer?
“Non-custodial” means that, unlike a custodial provider, we do not hold customer assets. However, this does not relieve us of responsibility.
We must operate within the applicable regulatory framework, maintain appropriate compliance procedures and collaborate with partners that meet our standards.
It is important to clearly define what the business does and does not do. Customers need to understand how the service works, and institutions need to know how the different parties fit together.
What would make you confident that the crypto industry has finally moved beyond the cycle of hype and speculation?
Companies should be judged more by the quality of their operations than by the market narrative surrounding them.
I would evaluate their ability to provide reliable services, establish long-term financial relationships and operate responsibly in various market conditions.
The industry will continue to experience cycles; that is normal. However, the companies that build for the long term are the ones that can continue to serve customers when the market is no longer providing easy momentum.
That’s the kind of business we want to build at Guardarian.
Looking ahead, how is the overall regulatory attitude towards the crypto industry shifting? What can we expect from both regulators and market participants over the next few years?
The narrative around crypto regulation has fundamentally shifted from reactive containment to proactive integration. Regulators no longer view digital assets as a fringe experiment but as an inevitable evolution of financial infrastructure that requires institutional-grade standards.
Over the next few years, we expect to see two key trends on both sides:
First is standardisation and passporting. Frameworks such as MiCA in Europe and VARA’s structured licensing in the UAE are setting global benchmarks. To prevent regulatory arbitrage, regulators in other key jurisdictions will likely align with these standards, making cross-border compliance more predictable for established players.
Second is the shift from viewing compliance as an obstacle to viewing it as a competitive advantage. For market participants, the days of simple licence-shopping are over. Priority access to tier-one banking rails and institutional financing will be granted to those who invest in strong governance, non-custodial efficiency and extensive compliance infrastructure.
In the coming years, convergence will define the landscape. Traditional financial institutions will adopt Web3 mechanics, and crypto infrastructure providers will operate with the same rigour, transparency and operational reliability as classical financial institutions.